
2026-11-03
Shelby PQC Gateway Series: Post-Quantum Security for Existing Enterprise Infrastructure
As quantum computing advances, organizations face a growing cybersecurity challenge known as “Harvest Now, Decrypt Later” — where attackers capture encrypted data today and store it for future decryption once quantum-capable computers become available. For industries such as healthcare, finance, telecommunications, defense, government, and critical infrastructure, sensitive data often needs to remain confidential for years or even decades, making post-quantum readiness an urgent priority.
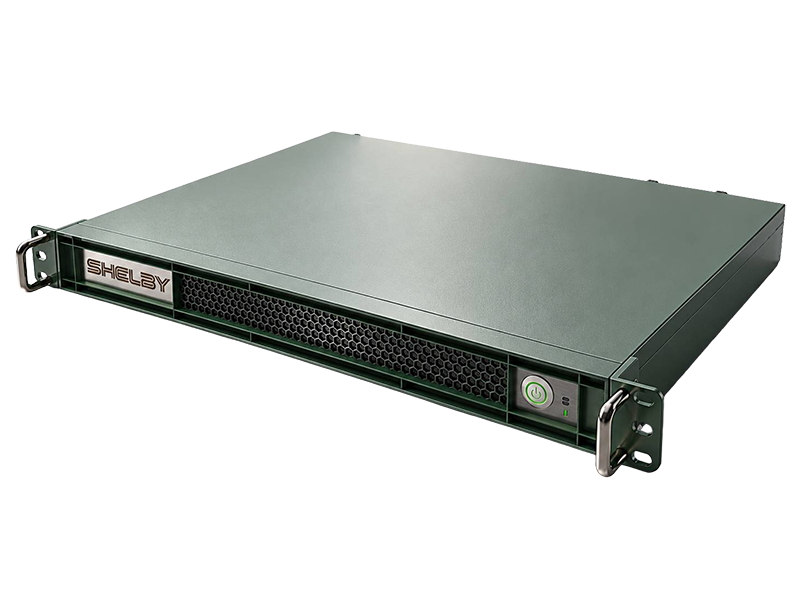
The Shelby PQC Gateway Series from ELGENS provides a practical and non-intrusive path toward post-quantum security. Designed as an edge gateway appliance, Shelby enables hybrid post-quantum TLS protection for existing infrastructure without requiring software installation, application changes, certificate re-issuance, or network-layer modification on protected servers. This allows organizations to upgrade cryptographic protection at the network edge while keeping existing systems intact.
At the core of Shelby is support for ML-KEM, standardized under NIST FIPS 203, combined with classical X25519 key exchange to provide hybrid quantum-safe protection. This architecture maintains compatibility with today’s TLS environments while preparing enterprises for the post-quantum future. According to ELGENS internal engineering tests, the hybrid ML-KEM handshake adds only approximately 2.3%, or about 2 ms, of latency compared with classical elliptic-curve TLS, while achieving a 100% success rate across 1,000 connection trials.
Built for mission-critical deployment, Shelby integrates TPM 2.0-sealed private key protection, Secure Boot, LUKS full-disk encryption, dual-plane hardware-bypass networking, and Active/Passive high-availability clustering. These capabilities help ensure that sensitive cryptographic material is protected while maintaining service continuity even in demanding production environments.
The finalized bridge-mode architecture allows Shelby to be inserted transparently between client-facing networks and existing server infrastructure. Non-intercepted traffic passes through normally, while protected TLS traffic is selectively handled by the Gateway for post-quantum TLS termination. In internal engineering validation, the bridge-mode architecture sustained 100,000+ concurrent connections with 0% failure, with additional endurance testing completing over 1.55 million fresh ML-KEM handshakes in five minutes.
Shelby is particularly suitable for sectors where direct server migration is difficult, costly, or operationally risky. This includes hospital systems, financial transaction gateways, telecommunications infrastructure, government communications, defense networks, and critical infrastructure environments. By moving post-quantum protection to the edge, Shelby helps organizations accelerate their quantum-safe transition while minimizing disruption to existing operations.
With the Shelby PQC Gateway Series, ELGENS delivers a field-validated, resilient, and scalable approach to post-quantum cybersecurity — helping enterprises protect today’s data against tomorrow’s quantum threats.